Australia’s cyber policy settings and public sector security debate are moving firmly towards Zero Trust, as agencies face pressure to prove not only that they are aligned to frameworks, but that they can see, contain and respond to threats in real time.
AI-enabled activity is changing the economics of the environment, allowing attackers to discover vulnerabilities at machine speed while defenders struggle with manual processes and incomplete visibility.
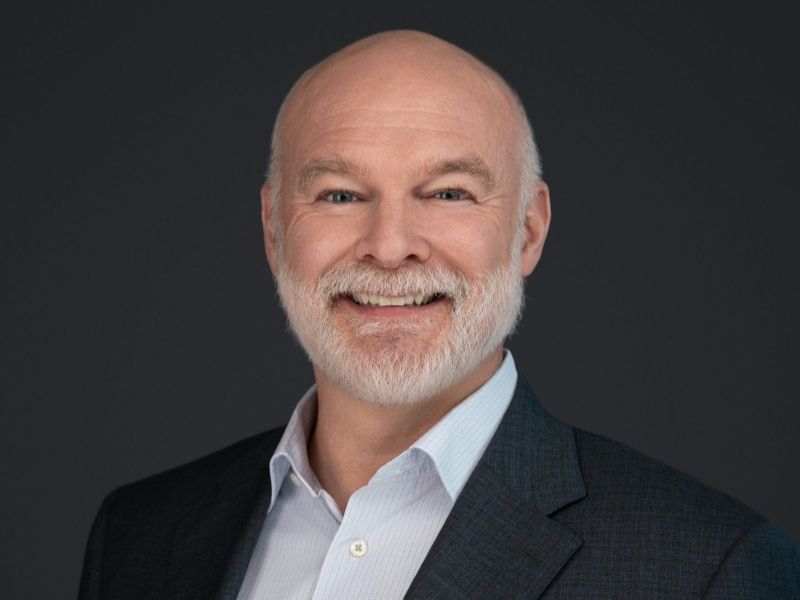
For Sean MacKirdy, area vice president of national security at Elastic, the problem is not that Zero Trust is outdated as a concept. It is that implementation can no longer afford to be slow, partial or compliance-led.
“Zero Trust as a principle is incredibly sound,” Mr MacKirdy told the Commercial Disco(very) podcast.
“The idea is to grant access only when there’s affirmative confirmation that a user, device or system should be trusted.”
That becomes especially important when attackers breach the perimeter. In a mature Zero Trust environment, they should not be able to move laterally through systems without repeatedly proving trust. This makes it much harder to carry out activities such as data exfiltration or command-and-control operations.
But there’s a catch.
“The challenge is that it has to be implemented comprehensively,” Mr MacKirdy said.
“Across the Five Eyes community, Zero Trust guidance has generally been introduced incrementally. Organisations were asked to implement foundational controls first, followed by more advanced capabilities over time.
“That phased approach is no longer sufficient.”
Mr MacKirdy’s perspective is shaped by a career at the intersection of technology, national security and geopolitics. His remit at Elastic includes the US Department of Defense, the US Intelligence Community, systems integrators, as well as Elastic’s public sector business in Canada, Australia and New Zealand.
Earlier in his career, he lived and worked through major geopolitical shifts, from post-Cold War Europe to the Middle East after the Arab Spring and Russia following the invasion of Crimea.
That experience has influenced how he views the current cybersecurity environment.
“Our cyber defenders – whether they’re in defensive cyber operations or intelligence agencies – aren’t just facing technical threats,” he said.
“They’re dealing with social, geopolitical and technological challenges all at once.”
The rise of AI has intensified that challenge. AI tools can be used to uncover vulnerabilities at machine speed.
If attackers can find vulnerabilities faster, agencies need security architectures that assume compromise is possible and limit the damage an attacker can do once inside. But this requires Zero Trust to function operationally, not just as a policy document or checklist.
Historically, Mr MacKirdy said, compliance has often been a periodic exercise.
“You’d ask questions like: Do you log unsuccessful login attempts? Do you maintain audit logs?
“Those activities help manage risk, but they don’t actually stop an attacker from entering your network or stealing data.”
Rather than simply recording a failed login attempt, a system should be able to trigger an immediate response, notify the relevant people and prompt remedial action where appropriate.
“It’s about responding proactively rather than simply recording events after they happen,” Mr MacKirdy said.
This shift away from static checklists is already reshaping Australia’s federal guidance, following the Australian Signals Directorate’s announcement that it will retire the long-standing Essential Eight framework over the next two years. In its place, the new Essentials series will transition organisations away from rigid maturity ladders toward a flexible, threat-informed defence posture.
The US Department of Defense has already moved in this direction. Mr MacKirdy said defence agencies were required to implement 92 Zero Trust controls by the middle of 2027, followed by 151 advanced controls within the following two years.
The most mature organisations are already working beyond those baseline requirements, bringing large language models into their cybersecurity operations to help analysts make sense of massive volumes of security data.
This is not about replacing human analysts. It is about changing the level at which they operate.
Security teams have traditionally arrived at work to find thousands of alerts waiting for review. The task was to search for meaningful patterns in enormous amounts of data –what Mr MacKirdy described as “finding a needle in a stack of needles rather than a needle in a haystack”.
In more advanced security operations, LLMs can analyse alerts, correlate them and map them against knowledge bases or frameworks like MITRE ATT&CK. Instead of presenting analysts with hundreds of disconnected alerts, the technology can identify that they relate to a single attack campaign.
“That’s the real shift,” Mr MacKirdy said. “It’s no longer about seeing individual alerts – it’s about understanding attacks.”
The foundation for this is telemetry: the signals generated across systems every time a user logs in, opens an application, triggers a firewall event or interacts with a network. Individually, these records may seem minor. At scale, they become impossible for humans to analyse unaided.
AI can process those signals at machine speed and identify patterns that matter. But it depends on agencies having the underlying visibility to support it.
“Organisations that have mature Zero Trust environments already have the telemetry needed to support that kind of proactive defence,” Mr MacKirdy said.
The human role remains essential. The point of AI-assisted defence is not to remove people from the loop, but to allow them to focus on higher-value analysis and response.
“The human remains absolutely critical,” he said.
“We’re not replacing cybersecurity professionals – we’re helping them focus on the signals that matter most.” Mr MacKirdy described this as moving the human “on the loop” rather than removing them from it.
The platform can investigate, correlate, and even propose a response plan, but a human analyst still validates the logic and approves the action before it takes action.
This matters because attackers are already using AI. Mr MacKirdy pointed to nation-state actors, organised crime groups and campaigns such as Volt Typhoon and Salt Typhoon as examples of adversaries using AI and machine learning to attack systems.
For defenders, that changes the equation.
Historically, attackers have had the advantage because they only need to find one weakness. Defenders need to protect the whole environment. AI-powered tools, combined with mature Zero Trust architectures, can help close that gap.
At Elastic, this is part of the thinking behind what the company calls an agentic Security Operations Centre – a model where AI helps defenders move from reactive alert handling to proactive investigation and response.
Increasingly, Zero Trust must extend into operational technology: the physical infrastructure systems, like power and water utilities, that citizens rely on daily. Many of these assets are decades old and use legacy protocols. However, as newer assets connect via Wi-Fi or Bluetooth, everything from smart building controls to rooftop solar panels expands the wider attack surface. Every connection must be brought into the Zero Trust framework.
For governments, the challenge is to prioritise quickly and pragmatically.
If Mr MacKirdy were a chief security officer in a government department, he would start by bringing industry and internal teams together to map risk.
Which assets matter most to citizens, and which services are critical to national resilience if disrupted? From there, governments must partner with industry to act at the speed of the threat.
“Governments can’t continue moving at the pace they traditionally have,” Mr MacKirdy said. “The reality is that the plane is already flying.”
That does not mean abandoning governance, auditability or human accountability. In public sector environments, those requirements are non-negotiable. But it does mean designing frameworks that allow agencies, local governments and service providers to act at the speed of the threat environment.
For Australia, the lesson is that Zero Trust should not be treated as a destination agencies will reach eventually. It is a security posture that needs to be made operational now.
The guidance may still be relatively new, but the world it was written for is already changing. AI has altered the speed of vulnerability discovery, critical infrastructure has expanded the scope of what needs to be defended, and geopolitical tensions have raised the stakes for cyber resilience.
Zero Trust remains one of the strongest frameworks for this environment – but only if it moves beyond compliance, beyond partial implementation, and into the day-to-day reality of how agencies monitor, detect, respond and recover.
As Mr MacKirdy said, the principle is sound. The urgency is what has changed.
This article was produced by InnovationAus.com in partnership with Elastic.
Do you know more? Contact James Riley via Email.